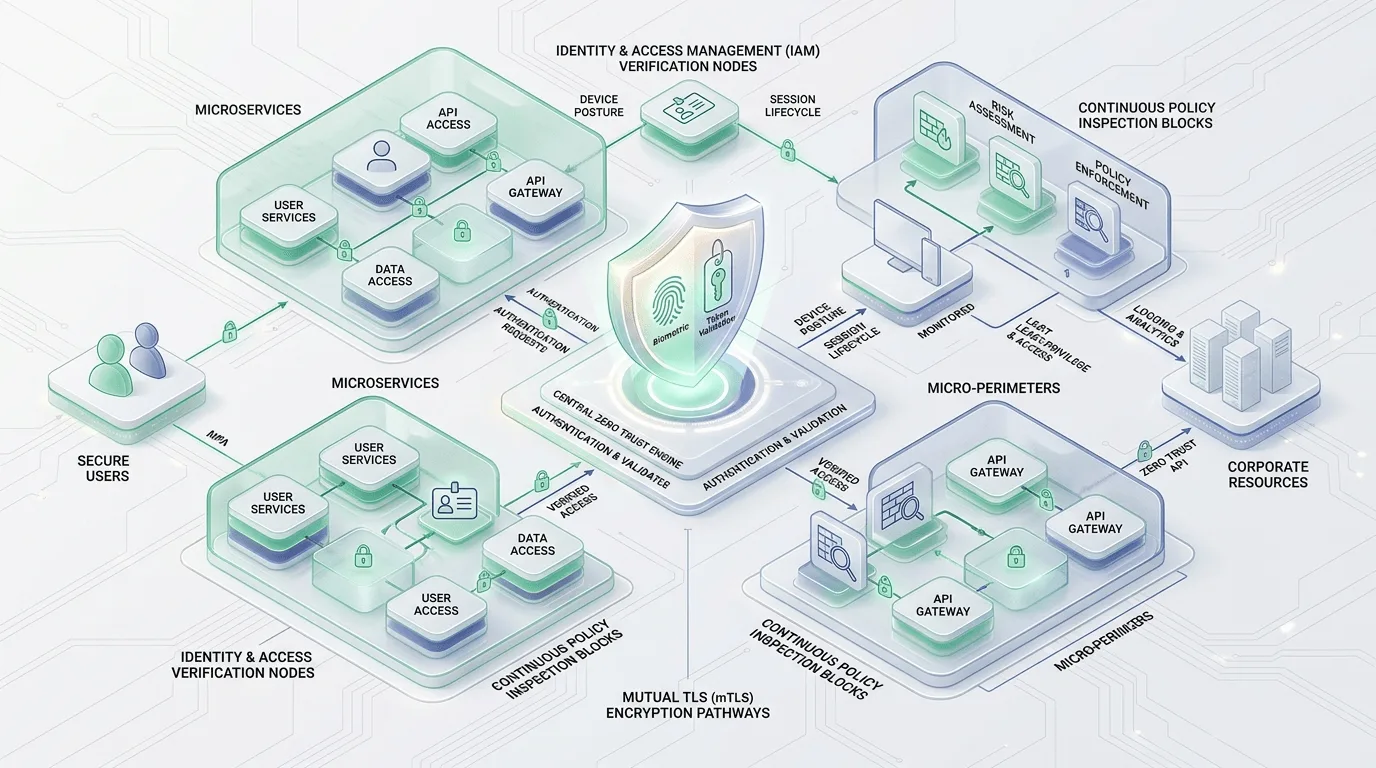
Zero trust sounds abstract until you translate it into application terms: never trust the network, always verify the request. Every call proves who it is and what it is allowed to do even inside your perimeter.
Three practices to adopt first
- Authenticate every request with short-lived, scoped tokens
- Authorize at the resource, scoped to the acting user
- Encrypt service-to-service traffic (mTLS) by default
Incremental wins
You do not need a big-bang migration. Start by scoping every data query to the authenticated user it closes the most common and most damaging class of vulnerability.